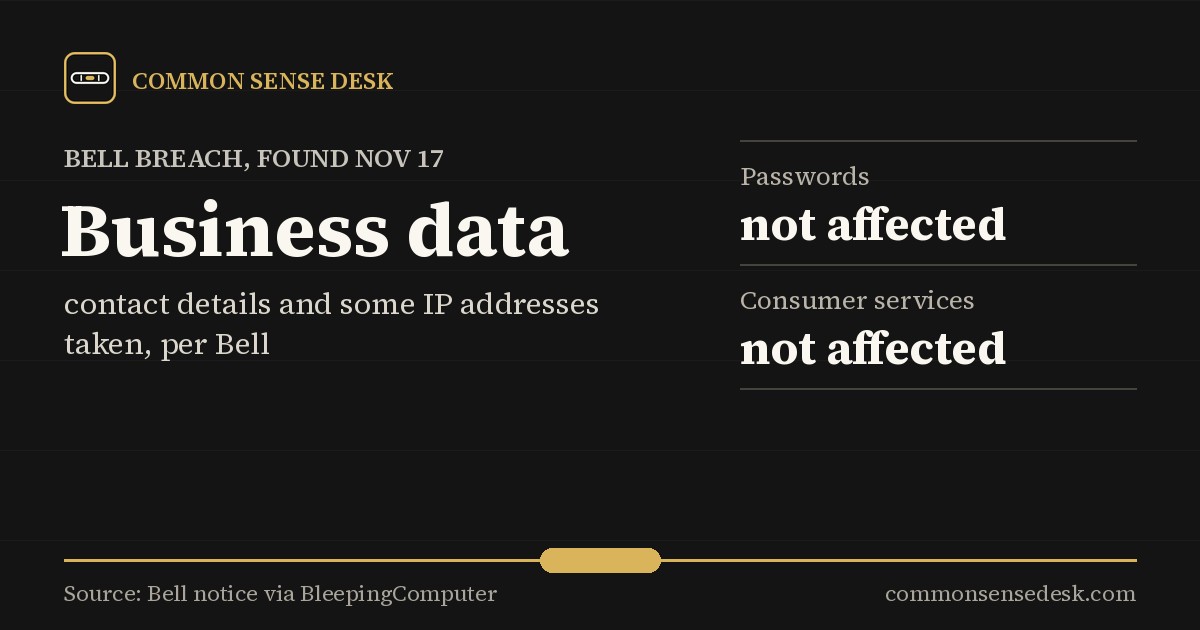
Bell Canada says hackers stole contact information belonging to some of its business customers in a cyberattack this week. The company says the attack hit a system it uses to order and set up network circuits for businesses, and that regular consumer services weren't affected, according to the tech news site BleepingComputer, which first reported the breach on Thursday, November 20.
Bell hasn't said how many business customers were affected.
What happened
According to a breach notice from Bell's information security team that a customer shared with BleepingComputer, an unauthorized party got into a pre-production, or testing, version of Bell's Maximo system on November 17. Maximo is software Bell uses to order and provision telecommunications circuits, the dedicated network lines that businesses rent for internet, phone and data links between offices.
Bell described the attacker as an "agentic" threat actor, a term that usually refers to hacking carried out with the help of AI tools that can take actions on their own, such as searching systems and pulling data automatically. Bell hasn't said who was behind it or how they got in.
The company says it has contained the incident and that there was no impact on customer services.
What was taken, and what wasn't
According to Bell's notice as reported by BleepingComputer and other security news sites, the data that may have been taken includes:
- business contact details such as names, job titles, work email addresses, phone numbers and business addresses
- titles of service tickets
- some IP addresses tied to network equipment or systems
- limited background information connected to those records
Bell said the affected data did not include passwords or other login credentials, highly sensitive personal information, or the PDFs and file attachments stored in the system.
Bell is contacting affected customers directly. It says it has also shared technical details of the attack with its enterprise customers and with the Canadian Centre for Cyber Security, the federal government's cyber agency.
Why business data matters
Names and work emails may sound harmless, but security experts warn that this kind of information is useful for scams aimed at companies. Someone who knows who manages a company's network, which circuits it has and what tickets it has open with Bell can send a very convincing fake email or make a convincing phone call pretending to be Bell or a vendor, and try to get a password changed or a payment sent.
The IP addresses of network equipment could also help an attacker map a company's systems, though Bell hasn't said whether that data was enough to be useful on its own.
A tough week for data security
The Bell attack is one of several this week that reached companies through outside systems or side doors rather than their main customer databases. On Thursday, a criminal group posted email addresses of thousands of JPMorgan Chase customers taken from the bank's marketing vendors, which we covered in our Chase story. Testing and pre-production systems are a common weak spot, because they often hold real data but get less protection than live systems.
Bell is Canada's largest telecom company, serving millions of consumer and business customers across the country.
The word "agentic" is new to most breach notices. It reflects a worry security researchers have raised all year: that AI tools able to run tasks on their own let attackers search and copy data from a system much faster than a person could. Bell hasn't given details on how the tool was used here, and that description comes from the company, not an outside investigation.
What it means for you
If you're a regular Bell home or mobile customer, Bell says this attack didn't affect you. If you work at a business that buys network services from Bell:
- Watch for a notice from Bell, and confirm it by calling your Bell account manager at a number you already have.
- Be careful with unexpected emails or calls claiming to be from Bell or a telecom vendor, especially ones asking for passwords, network changes or payments.
- Ask your IT team whether any of your network addresses were in the affected data and whether extra monitoring makes sense.
Bell hasn't said whether it reported the breach to the federal privacy commissioner. Companies in Canada are required to report breaches that pose a real risk of significant harm to individuals.
What to watch
How many business customers were affected, who carried out the attack, and whether any of the stolen data shows up for sale online.
Sources
- BleepingComputer: Bell Canada says 'agentic' hacker stole enterprise customer data (Nov. 20, 2026) bleepingcomputer.com